VMware Cloud Foundation (VCF) gives platform teams one platform and one operating model for VMs and containers, with VKS providing CNCF-certified Kubernetes built directly into VCF. As clusters move into production, networking and security become the hard part: pod IPs change in seconds, static firewall rules stop matching, and troubleshooting means digging through node logs. Calico Enterprise solves this as a native VKS add-on, installed, upgraded, and reconciled on the same lifecycle as the cluster. VCF networking owns the VPC and north-south traffic, while Calico Enterprise owns east-west traffic down to the pod and namespace, with policy tiers, microsegmentation, flow logs, and policy recommendations. This lets customers retire the second Kubernetes distribution some still run on vSphere and consolidate on VKS.
As AI moves onto VCF, a new kind of workload is landing on VKS clusters: AI agents. Lynx extends Tigera’s security to these agents, so platform teams can offer them as a supported workload with identity, policy, and containment built in. Together, Broadcom and Tigera give platform teams a validated path from cluster networking to zero-trust security, observability, and AI agent security at enterprise scale.
Run AI agents on VKS. Stay in control.
Tigera Lynx secures AI agents running on Kubernetes, giving platform and AI teams the visibility, control, and runtime enforcement they need in production on VKS.
AI agents are already arriving on enterprise Kubernetes platforms, and VKS clusters are no exception. A tenant deploys an AI agent like any other workload, and nothing marks it as one. At runtime the agent chooses which models, MCP tools, and other agents to call, usually on someone’s behalf. Rules written for known services can’t anticipate that, and a valid credential is no guarantee of good behavior.
Lynx makes AI agents a supported workload on VKS instead of an exception to it. It runs inside your clusters, so platform teams can offer agents as a paved road, AI teams get the access they need to ship, and security can say yes with a record to back it up.
82% of organizations found at least one AI agent or workflow their security or IT team didn’t know about in the past year.
—Cloud Security Alliance, April 2026
See the Agents You Didn’t Know About
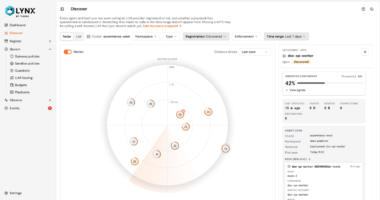
eBPF auto-discovery finds AI agents in your VKS clusters by behavior, registered or not, and cross-references them against a central agent registry so shadow agents surface. Platform teams know which tenants run agents before anyone has to ask.
Govern Every Call
Every agent-to-LLM, agent-to-MCP, and agent-to-agent call passes a Lynx checkpoint and runs only if policy says this agent may make this call, for this user, right now. Each agent gets a verifiable identity from the source you already trust: Okta, Entra ID, and your existing IdPs, with SPIFFE/SPIRE SVIDs for workload identity.
Contain Any Agent
Some agents try to go around the Lynx checkpoint. eBPF enforcement on the node catches them. Every agent starts from default-deny, with scoped tokens and its own sandbox, so one mistake stays small. If an agent misbehaves, you can quarantine just that agent, and the rest of its tenant keeps running.
Prove Every Action
A per-call audit record and OpenTelemetry traces show which agent did what, for whom, and why it was allowed. Nothing Lynx records leaves your estate.
How Lynx fits on VKS
- Runs in your clusters. Lynx deploys into your VKS clusters with Helm, separate from the VKS Add-on Framework. It is not a hosted service.
- Alongside your existing CNI. Lynx doesn’t replace the cluster’s CNI. It runs next to whichever one your VKS clusters use.
- No agent code changes. Nothing to rewrite. New agents ship into limits security has already agreed.
- Built on open standards. SPIFFE/SPIRE, Cedar, MCP, A2A, and OpenTelemetry.
Better together with Calico Enterprise
Calico Enterprise and Lynx work at different layers. Calico Enterprise isolates model and agent workloads and controls their egress at the network level. Lynx governs what each AI agent is allowed to do, call by call, and contains it when it steps outside policy. Run Lynx on its own, or pair it with Calico Enterprise for defense in depth on VKS. Both come from Tigera, the founders and maintainers of Project Calico.